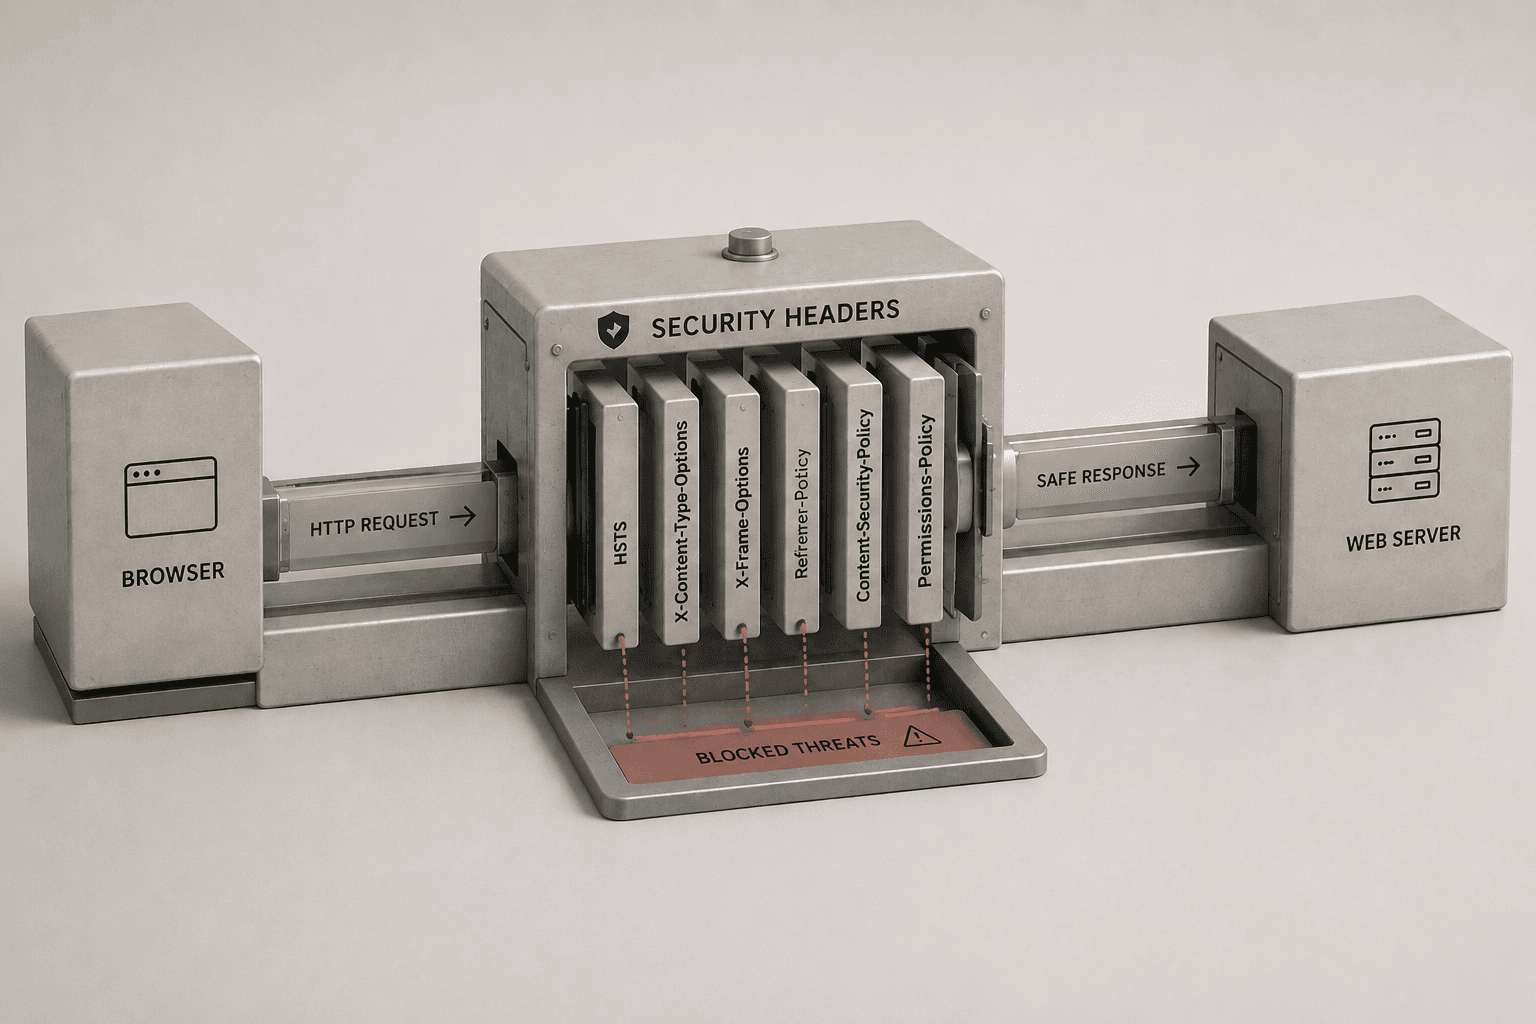
When you visit a website, the content you see on screen is only half the story. Behind the scenes, the web server sends invisible metadata known as HTTP response headers. While many headers simply control caching or identify the server, a specific subset called security headers forms the frontline defense against modern web vulnerabilities.
What Are HTTP Security Headers?
Security headers are directives sent by a web server that instruct your browser on how to behave when handling the site's content. By configuring these headers correctly, website administrators can instantly lock down their applications against common attacks like Cross-Site Scripting (XSS), clickjacking, and data injection.
If a site fails to implement these headers, the browser falls back to its default behavior. Unfortunately, default browser behavior is designed for maximum compatibility with old websites, which often leaves modern users exposed to risks.
The Most Important Security Headers
While there are dozens of possible HTTP headers, these six are widely considered essential for any secure web application:
1. Strict-Transport-Security (HSTS)
HSTS forces the browser to only connect to the website using secure HTTPS connections, completely ignoring any attempts to load the site via unencrypted HTTP. This prevents attackers on public Wi-Fi networks from intercepting your connection and downgrading it to an insecure state.
2. Content-Security-Policy (CSP)
CSP is arguably the most powerful security header. It allows the server to declare exactly which domains are allowed to load scripts, images, and stylesheets on the page. If a hacker manages to inject a malicious script into a comments section, CSP will block the browser from executing it because the script's source is not on the approved list. This is the primary defense against Cross-Site Scripting (XSS).
3. X-Frame-Options
This header prevents your website from being embedded inside an iframe on another domain. Attackers use iframes for "clickjacking" — a technique where they load your site invisibly over a malicious site, tricking users into clicking buttons (like transferring funds or deleting an account) on your site without realizing it.
4. X-Content-Type-Options
Historically, if a server didn't declare what type of file it was sending, the browser would try to guess (MIME sniffing). Attackers exploited this by uploading malicious executable scripts disguised as harmless images. Setting this header to `nosniff` forces the browser to strictly follow the declared content type.
5. Referrer-Policy
When you click a link to leave a website, your browser tells the new site exactly where you came from using the Referer header. If you are on a page with sensitive data in the URL (like a password reset token), this data can leak to third-party sites. Referrer-Policy controls exactly how much routing information is shared.
6. Permissions-Policy
Previously known as Feature-Policy, this header allows site owners to explicitly disable access to hardware features. For example, a blog can declare that no scripts on its pages are allowed to access the user's microphone, camera, or geolocation.
How to Check a Website's Headers
You do not need to be a developer to audit a website's security. You can inspect the raw response headers of any web server using our HTTP Headers Checker tool. Simply paste a URL, and the tool will analyze the response to see if these critical protections are in place.